
Concordia: a day with our clients and partners
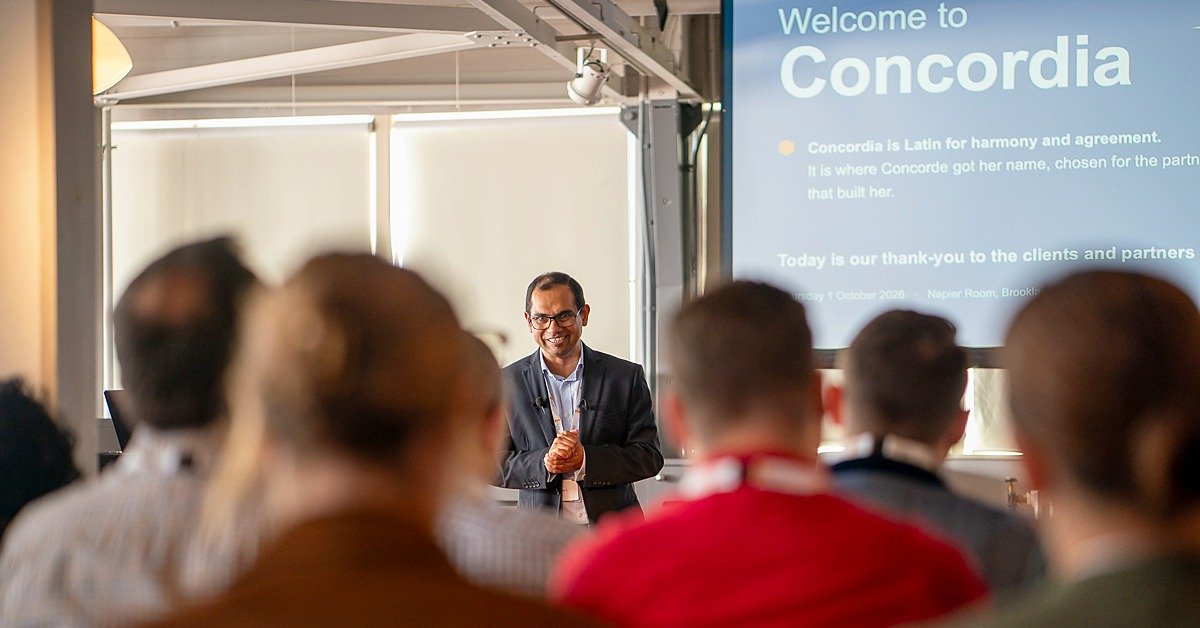
On 1 October we welcomed our clients and partners to Brooklands Museum for Concordia, our way of saying thank you to the people we work alongside. Concordia is Latin for harmony and agreement. It is also where Concorde got her name, chosen for the partnership that built her, which felt like the right fit for a day about working together.
The day mixed practical cyber security thinking with time to talk, eat well and enjoy one of the most remarkable settings in the country. Here is what we covered.
Our journey, and what we are seeing
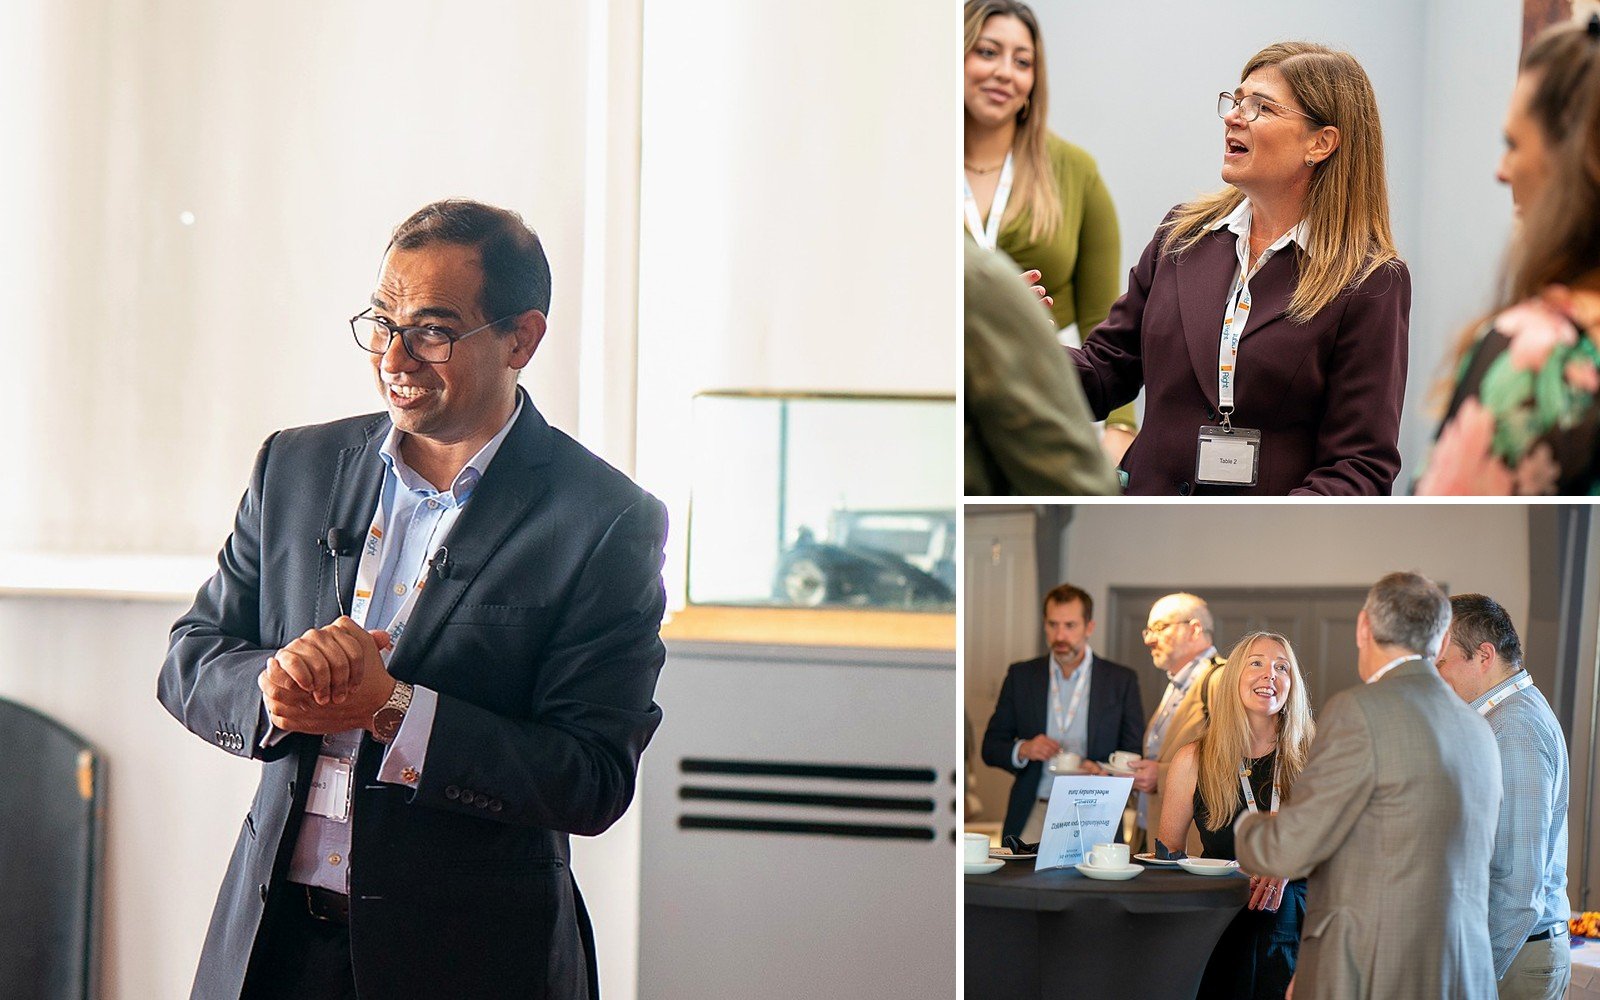
Yogesh Agarwal, our CEO, opened the day with the RightCue story: starting out in 2009, becoming one of the first certification bodies for Cyber Essentials, and growing into an NCSC Assured Cyber Security Consultancy and a certification body for Defence Cyber Certification. Along the way, he thanked the clients and partners in the room for helping us grow.
He made a point we hear in almost every client conversation: organisations are rarely trying to solve a cyber security problem on its own. The real pressures are compliance, knowledge and resources, delivering change across teams, and deadlines.
He then walked through six shifts we are seeing across our client work: identity as the new perimeter, the rise of the bots, the supply chain as the weakest link, tougher rules and regulation, the move from cyber security to cyber resilience, and the human side of cyber. Guy Marong added a practical reminder from his time dealing with attackers at Sony: there is no security without a bad guy somewhere, so plan for how a motivated attacker would actually get in.
A live incident exercise
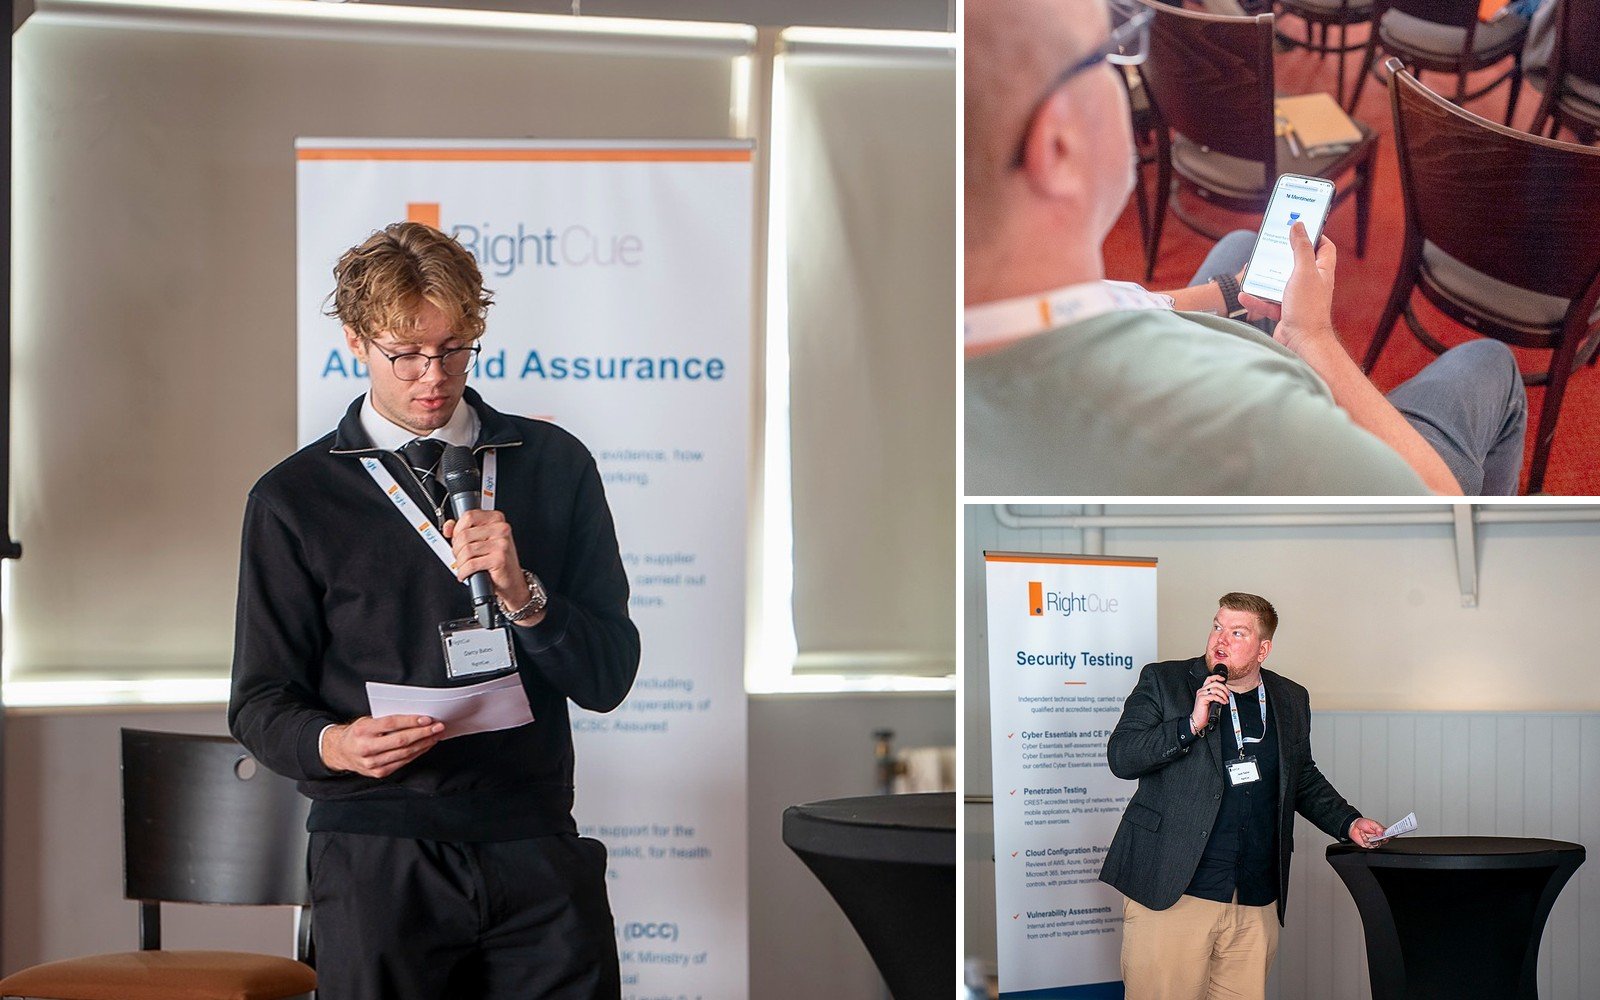
Our team then took the room through a live incident at a fictional company, Meridian, over three days. Guests voted on their phones at each stage: spotting the first warning signs on a Friday afternoon, deciding who leads when the CEO is unreachable, handling a deepfake request for an urgent payment, meeting the 72-hour deadline to report to the ICO, warning customers, and working out why a clean penetration test had not caught the way the attackers got in.
The room got almost every answer right. The closing questions were the ones to take back to the board, including who leads your response if your CEO is on a plane, and when your leadership team last rehearsed its plan. We will share the full scenario in a white paper on the Knowledge Hub.
The panel: a new convergence point
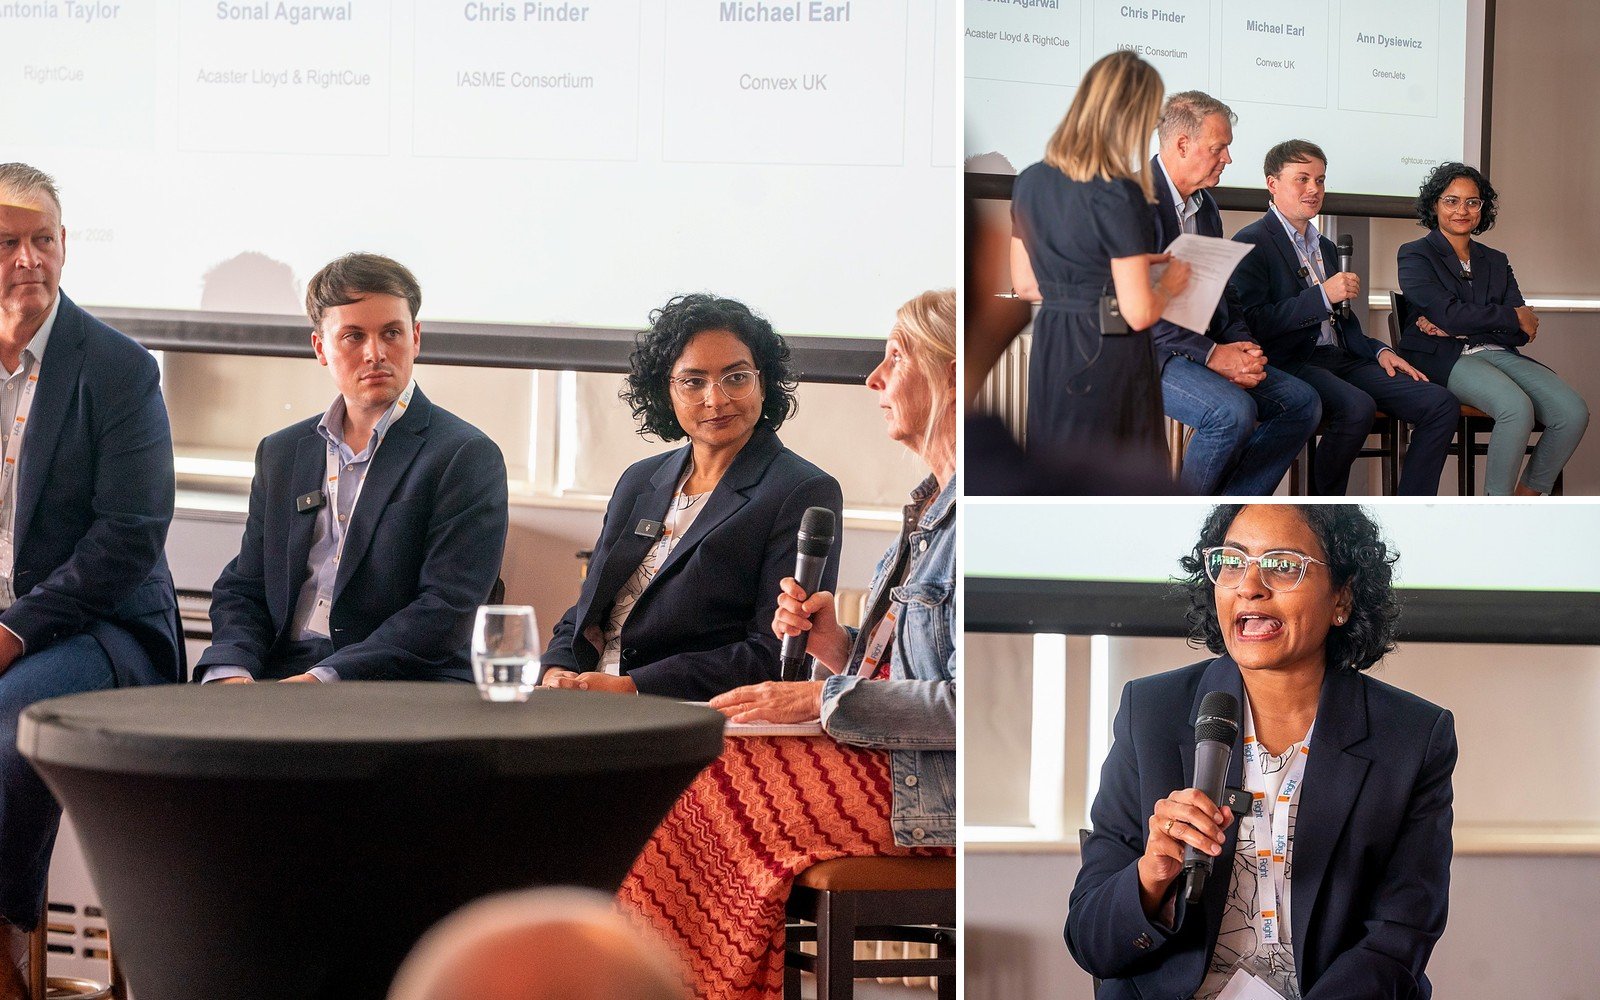
Our panel looked at how security, AI governance, compliance and certification are coming together, and what that means for the people responsible for them. Antonia Taylor chaired, with Chris Pinder of IASME, Michael Earl of Convex, Sonal Agarwal of Acaster Lloyd Consulting, and Ann Dysiewicz of GreenJets.
The conversation covered why this is convergence rather than collision, how AI is speeding up the way things are built and why governance has to keep pace, the value of one set of controls mapped to every framework instead of the same audit five times a year, and why culture and visible leadership decide how ready an organisation really is. Questions from the floor took in scheme equivalence, Defence Cyber Certification and how Cyber Essentials might evolve for AI.
“DCC is by a country mile the most significant compliance standard we’ve undertaken, and is the only one that I felt safer for having gone through.”
A client, speaking from the floor during the panel Q&A
We are turning the discussion into a white paper, The New Convergence Point, which will be published on the Knowledge Hub soon.
Lunch and one-to-one time with our consultants
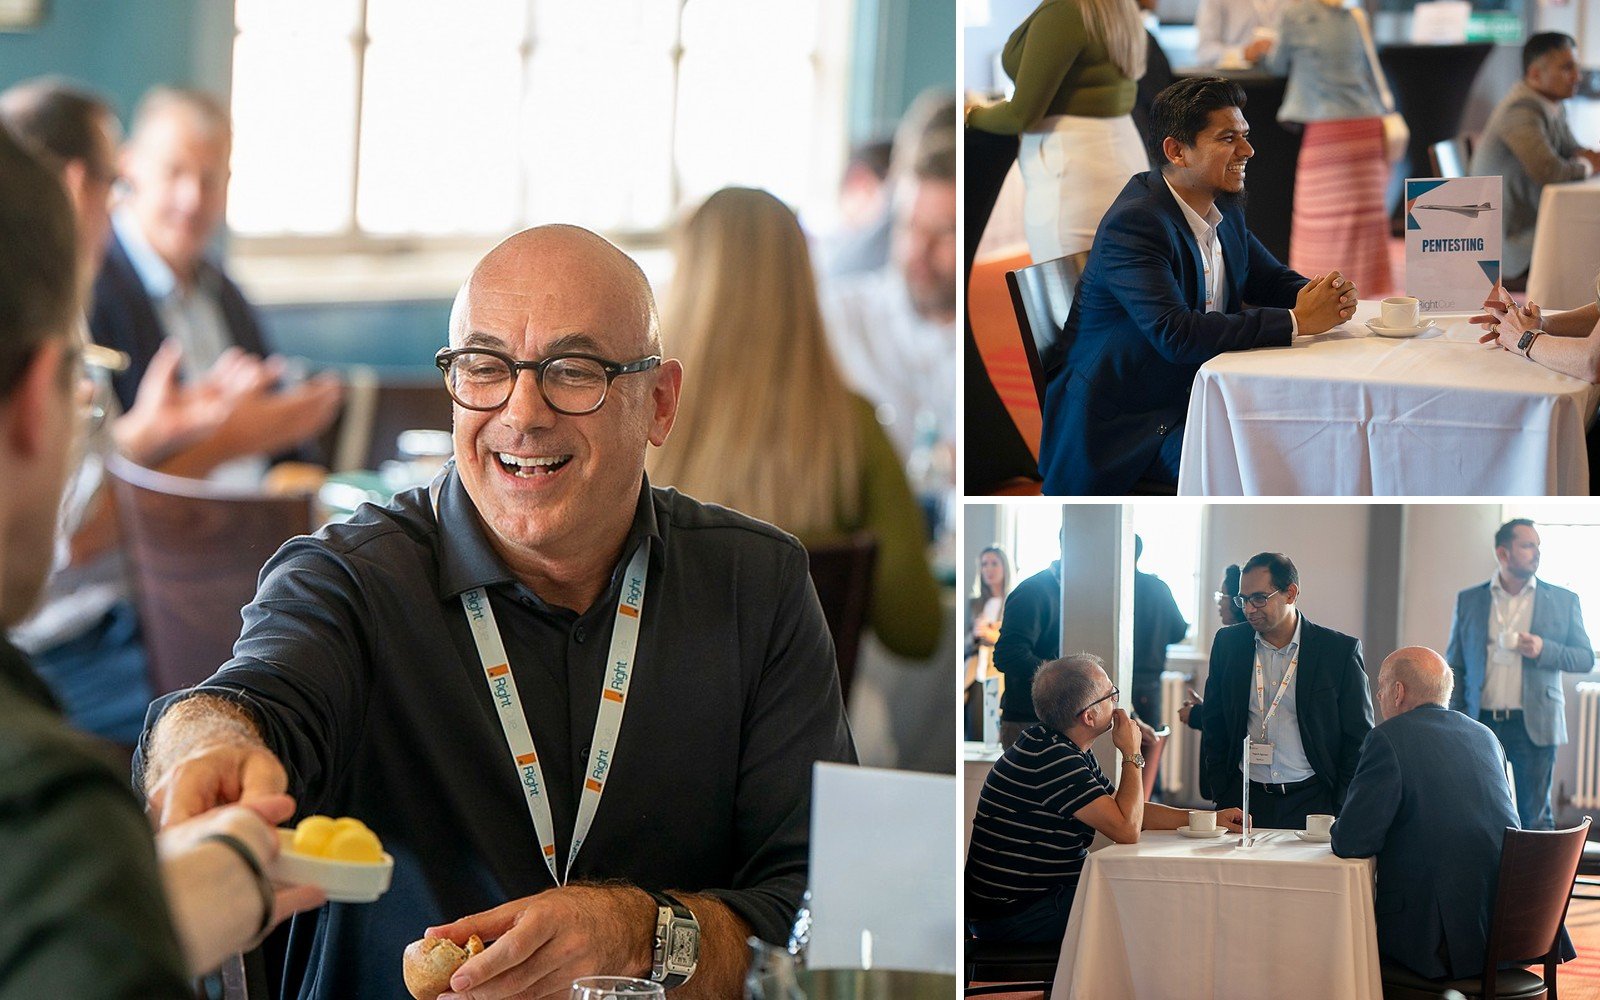
After a three-course lunch in the Bluebird Room, the afternoon was for guests to shape. Our consultants hosted one-to-one tables on GDPR and data protection, cyber incident exercising, Cyber Essentials and Defence Cyber Certification, supplier risk, penetration testing, and a general table with Yogesh. These conversations are where the day turns into practical next steps, and it was great to see every table busy.
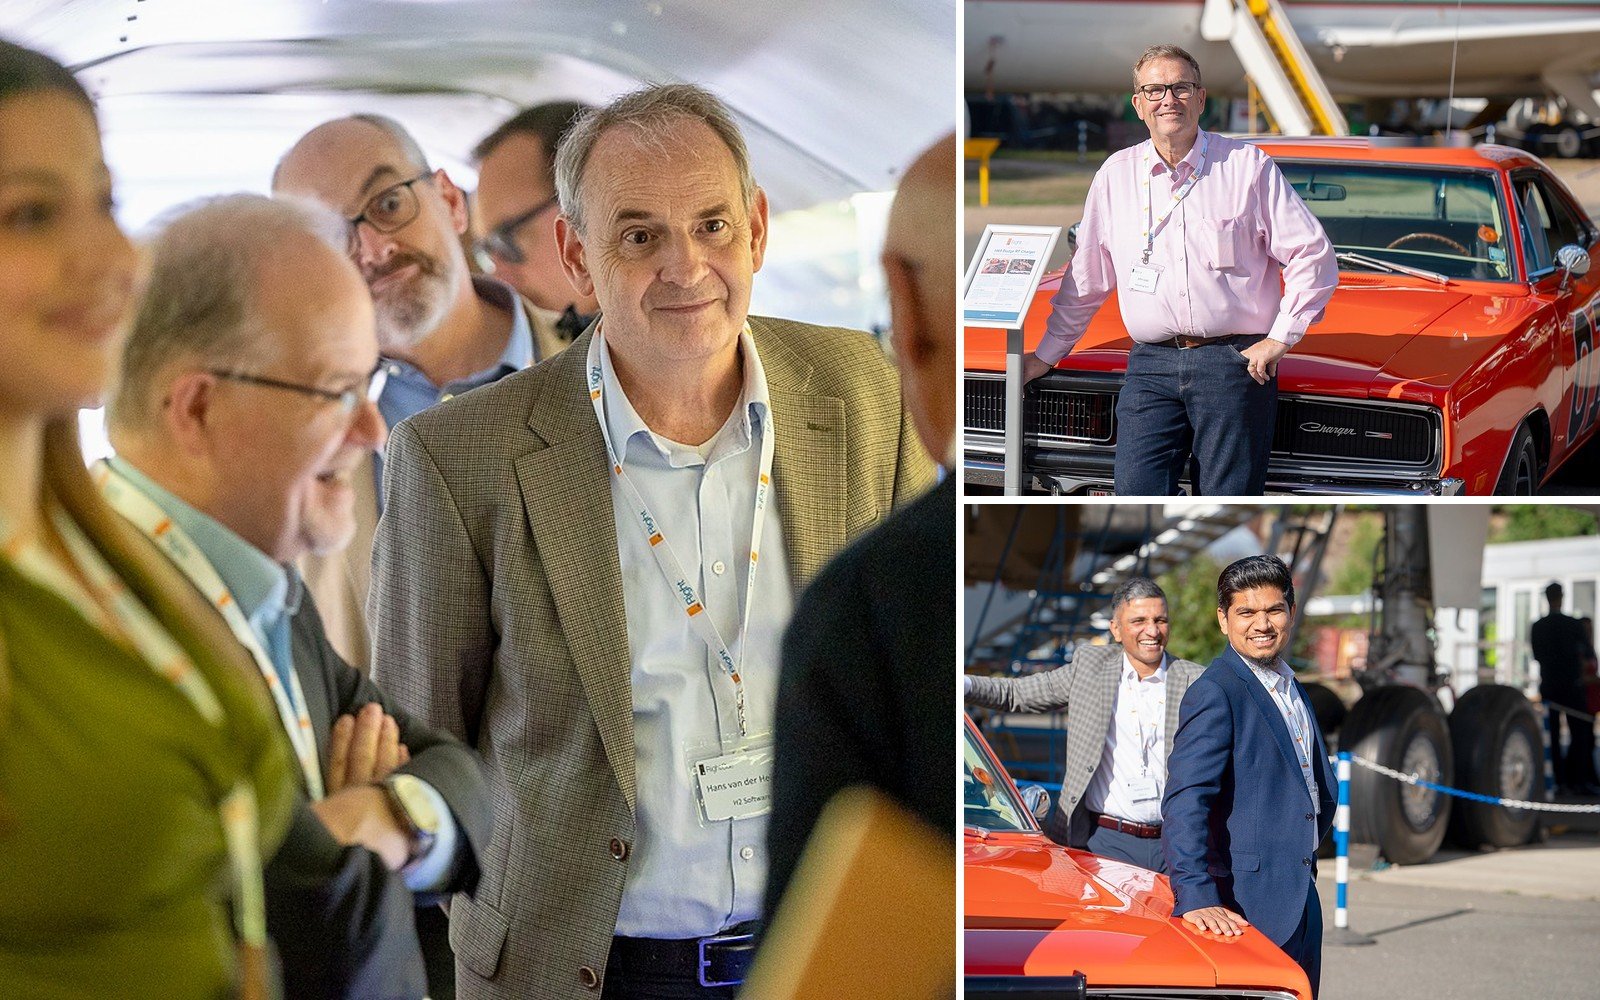
Concorde and a 1969 Dodge Charger RT at Brooklands
Guests then had a private session on board Concorde, with plenty of happy faces coming back down the steps. Parked alongside was a 1969 Dodge Charger RT, kindly brought along by John, which drew a crowd all afternoon.
“Even the Dukes of Hazzard’s General Lee was there to greet us! If you’ve not been, the museum is top notch and to walk onto Concorde is the icing on the cake.”
Chris Pinder, IASME
What our guests said
Some of the kind words guests shared on LinkedIn after the day.
“Sessions covering AI were a little scary. A reminder that security, compliance and AI can no longer be treated as separate conversations. Thanks to the team for an eye opening event.”
Simon Adams, Managing Director, PRD Technologies
“Taken home some great insights into compliance and AI security. Even got a ride on Concorde!”
Chris Pain, Head of Information Technology, Evorio
“Fantastic day, learning about AI security and compliance. Topped off with geeking out over some military planes and a trip onboard Concorde.”
Gary Deighton, Key Account Manager, Evorio
Thank you

Thank you to everyone who joined us, to our panellists, to the team at Brooklands Museum, and to the RightCue team who made the day happen. Nothing we do works without the clients and partners in that room.
Over the coming weeks we will be sharing more from Concordia, including a six-part series on the shifts we are seeing in cyber and our two white papers. If anything from the day would be useful for your organisation, get in touch at rightcue.com.